Product
Platform
Products
More
Resources
Company
Product
Platform
Products
More
Resources
Company
Product
Platform
Products
More
Resources
Company
The Preemptive Cybersecurity Platform
Trusted by pioneers in prevention




How it works
Profile threat actors, their TTPs and intent before they target you. Intelligence comes first.
Map that intelligence to your assets, identities and real attack surface: what is actually exposed to what.
Surface what matters the moment it matters. Only relevant coincidences between threats and your environment. No noise, no delay.
Turn signal into action across your existing stack autonomously. No manual triage. No ticket queue.
Reduce Exploitable Risk
Discovery, validation and exploitation now run at machine speed. The time an exposure stays exploitable is the number that has to come down.
Preemptive Cyber Operations is how we do it.

Machine-Speed Defense
Ask NINA anything about your environment, a threat actor, a leaked credential, a suspicious file. Get back an answer with cited sources and a workflow that acts on it, with every step visible and the choice to step in yours.
Explore NINA AI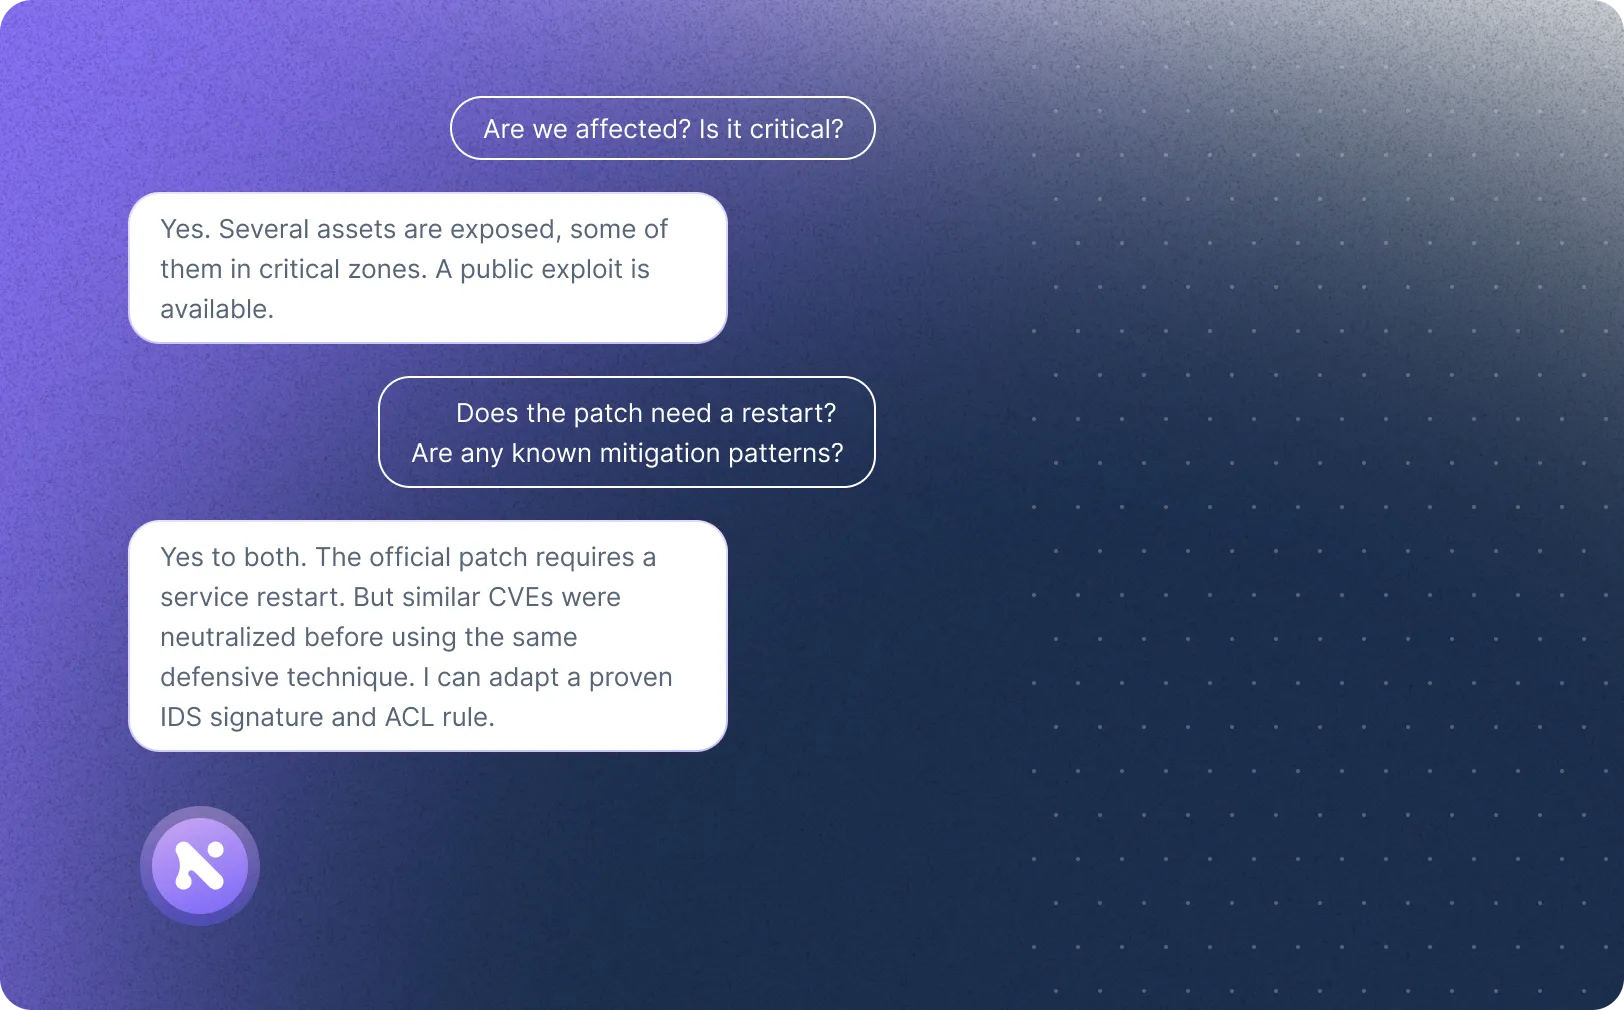
Automation Workflows
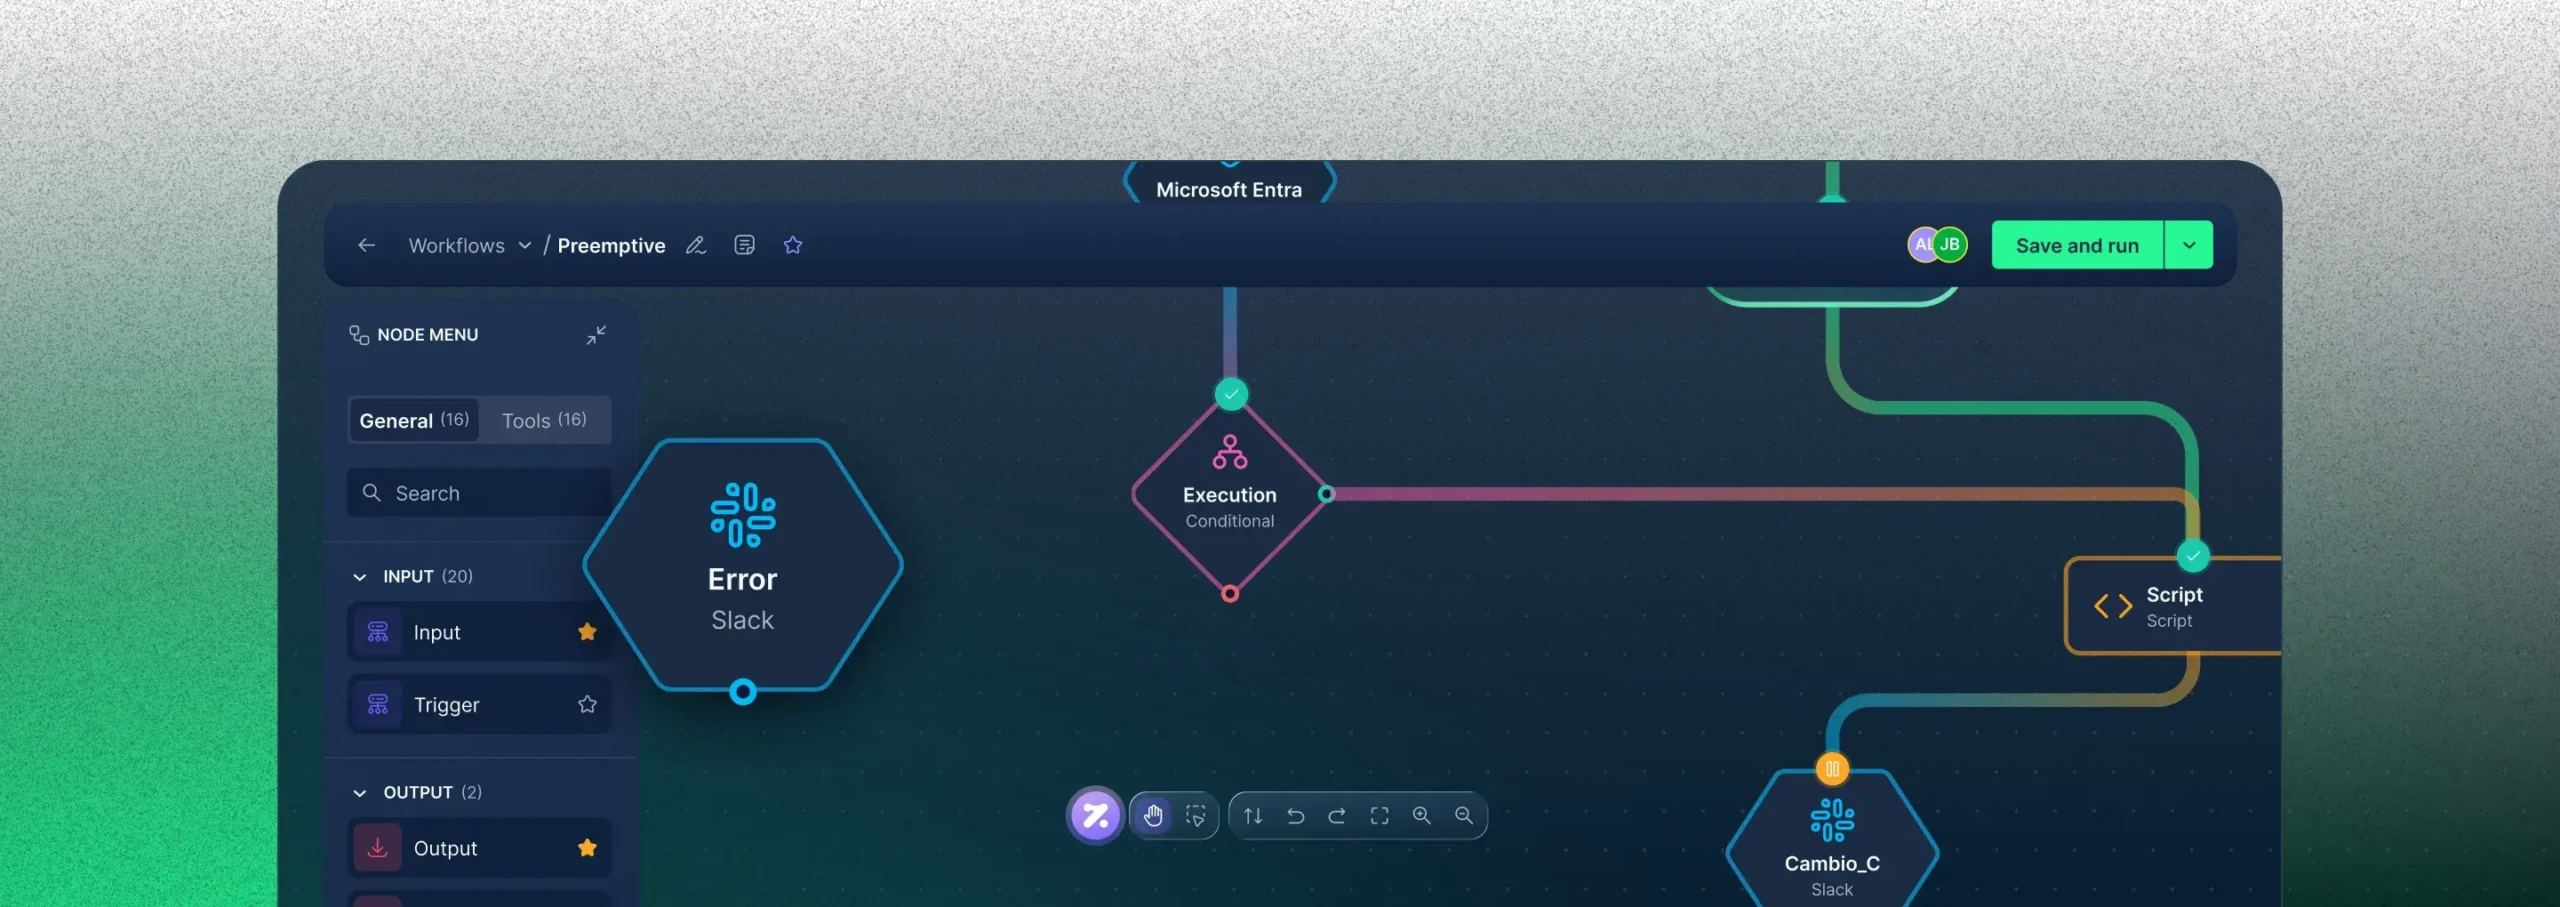
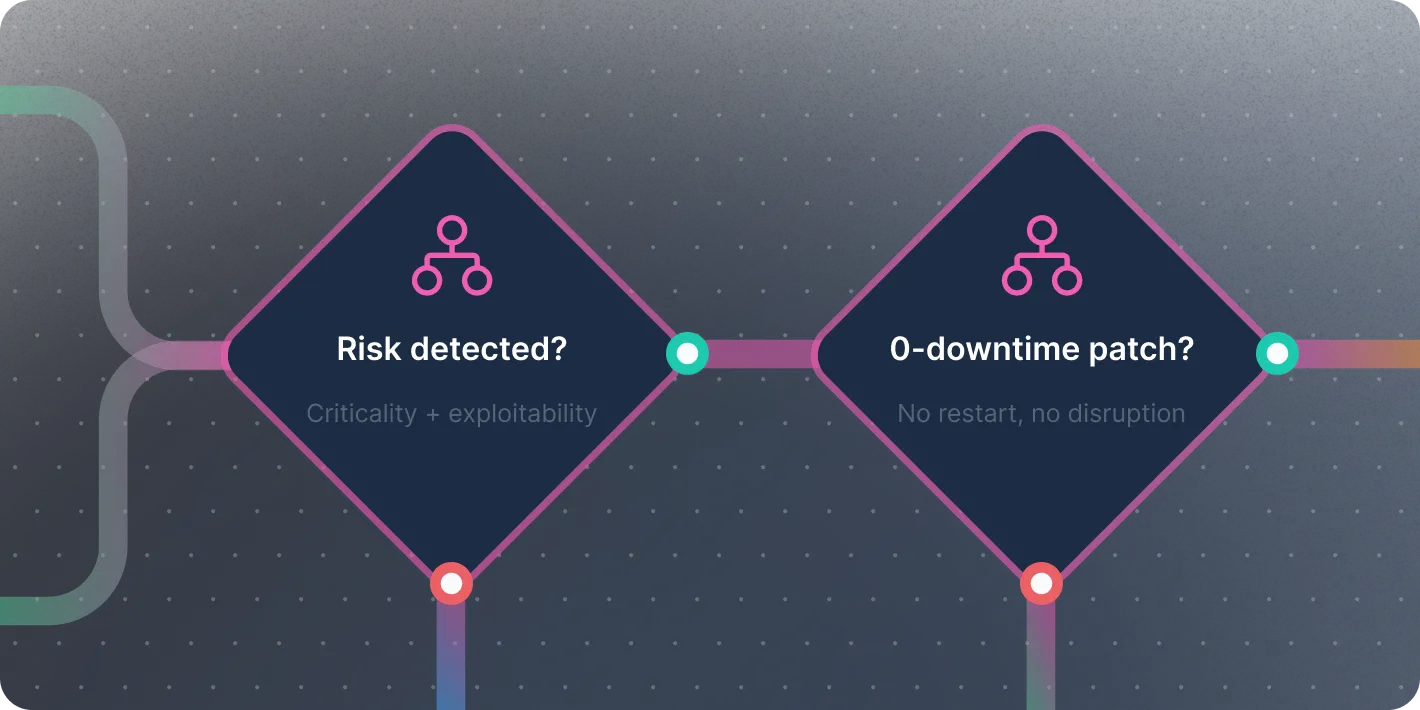
Zynap gives you a visual canvas and 75 tool nodes to build workflows on, putting your offensive, defensive and intel teams in the same operational layer.
Explore
Threat Intelligence
Zynap correlates 900+ threat actors and campaigns against your own exposures, identities and third parties, so analysts on investigate instead of triage.
Explore
Credentials Intelligence
Zynap detects 600M+ credentials a month and validates which of them still work, cutting your team's list down to the exposures that are live right now.
Explore
Sandbox
Zynap detonates suspicious files in its own sandbox maps the behavior MITRE ATT&CK, and feeds the indicators into the workflows you already run.
COMING SOON
Zynap's Results
600M+
Credentials detected monthly
900+
Threat actors and campaigns
300K+
CVEs profiled and risk-scored
2M+/mo
Infected devices monitored monthly
Our Solutions
One operational layer for every client.

Multi-tenant by design
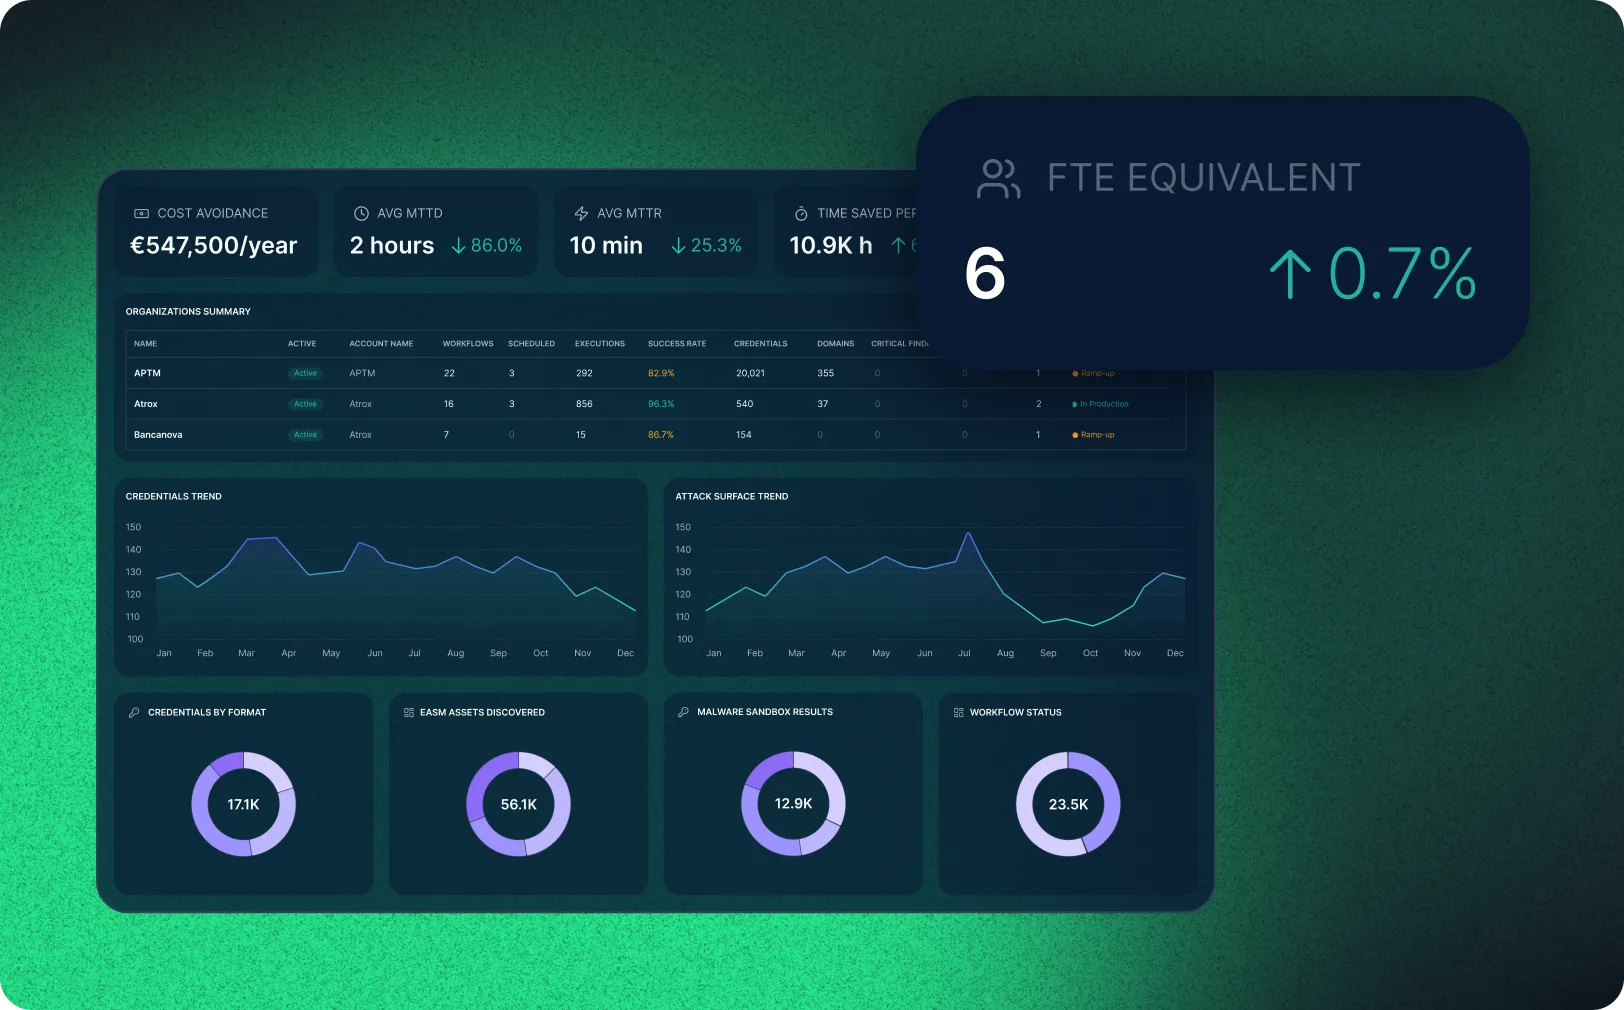
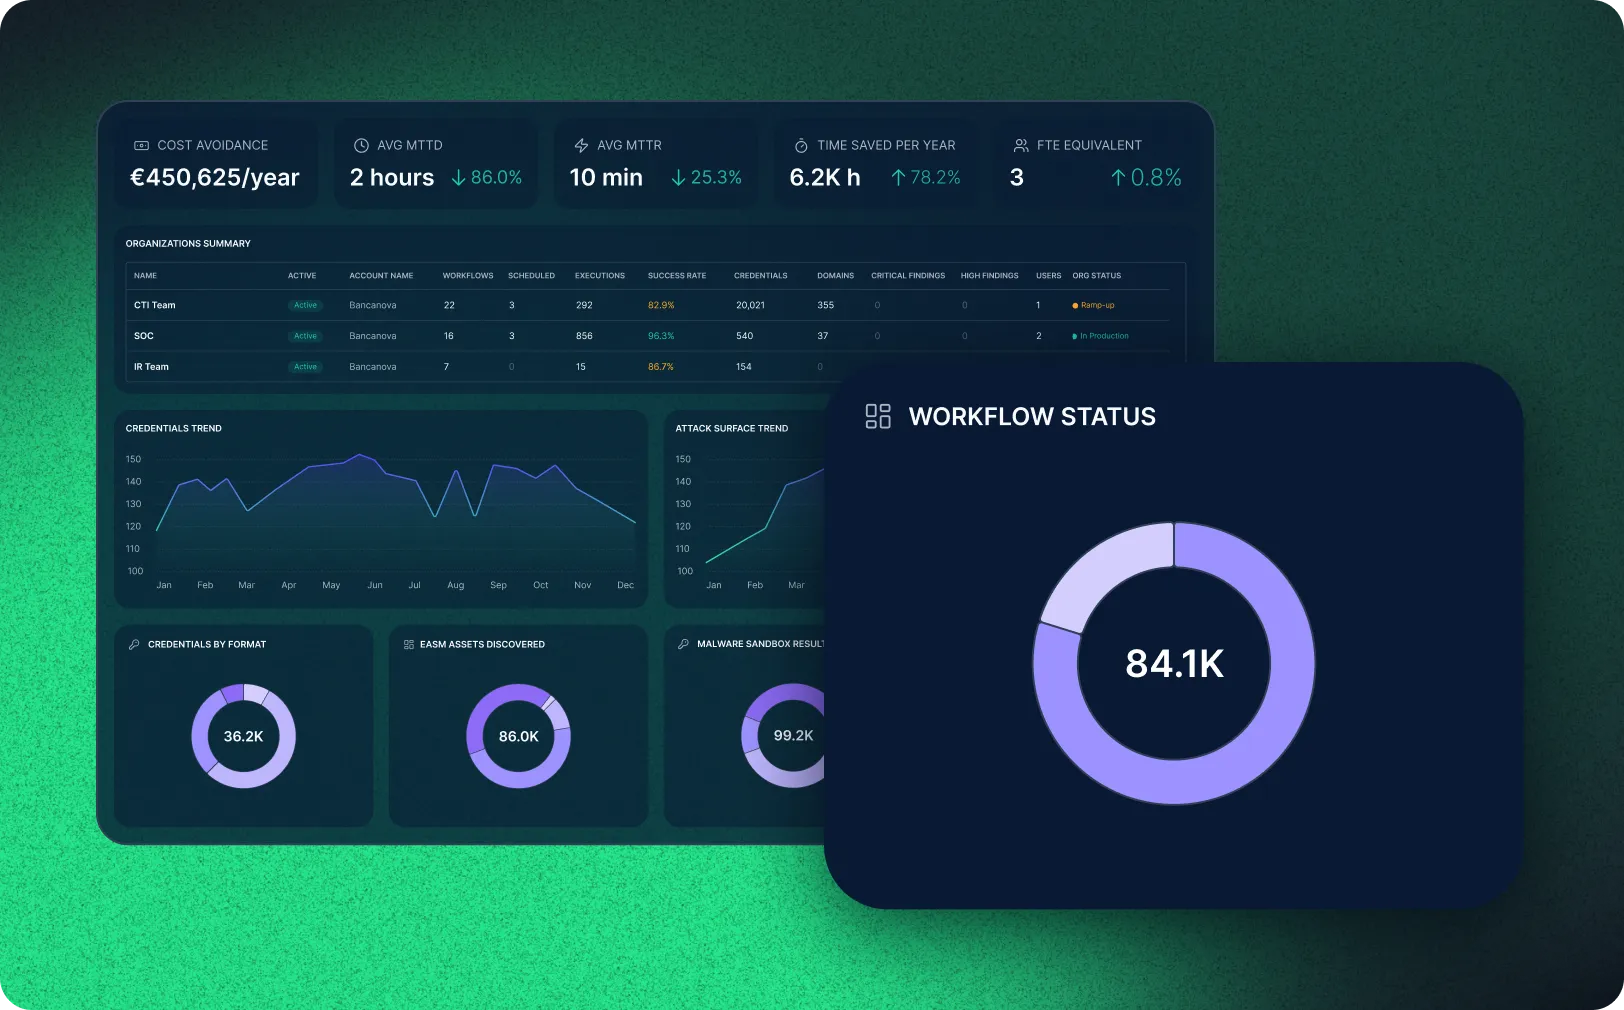
Each client's data stays in its own tenant. Build a workflow once, run it across the portfolio, and see everything from one dashboard.

New revenue streams
End shrinking margins and capped profitability. Faster onboarding from a use-case library gets new tenants live in days, freeing your team for higher-margin services.

Preemptive defense at scale
Bring down MTRER, Mean Time to Reduce Exploitable Risk, and threats are neutralized in the live environment before the patch arrives.
Not your team built gets replaced.

Threat context at scale
Stolen credentials, active malware and the actors using them, matched against your live environment. That pulls MTRER (Mean Time to Reduce Exploitable Risk) down.

Same team, more coverage
Multiply what your team can defend. More assets, more identities, more attack surface, without them working longer or burning out.

Governed at every step
Versioned workflows, approval gates and rollback, with every automated action and every human decision traceable for DORA, NIS2 and the AI Act.
Customer Stories


Our integrations